Non-3DS Card Payment
In this page, you will learn how to create payments through the Non-3DS card payment API in a few steps:
- Collect your client's payment Information.
- Trigger OPay Non-3DS card payment API with your collected information.
- Handle the API Response.
- Redirect your client to Non-3DS cashierUrl.
- Redirect your client to returnUrl after the payment is completed and to cancelUrl when the payment is canceled.
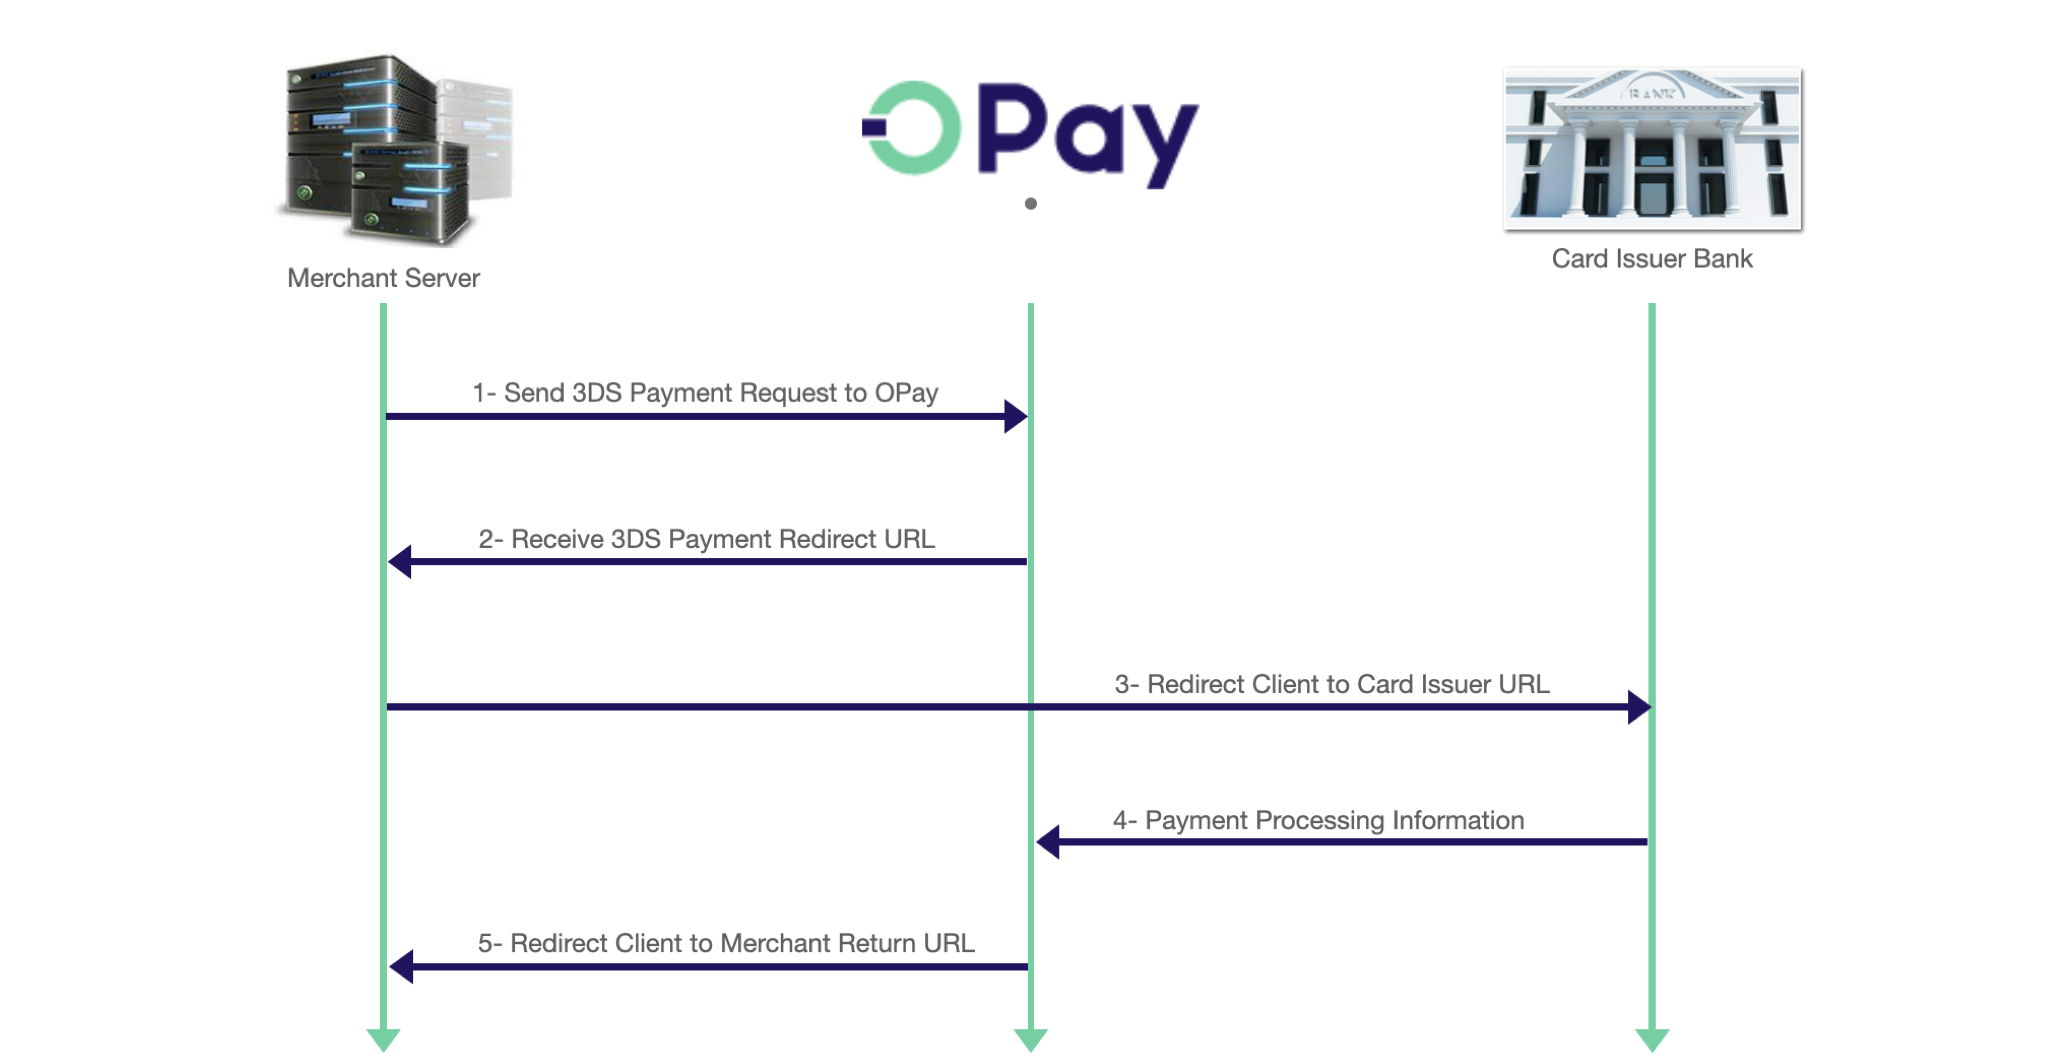
it works as follows:
- Merchant will send Non-3DS Payment request with client information and returnURL to OPay.
- OPay will respond to the merchant with redirectURL to the Card Issuing Bank.
- Merchant will redirect the client to the bank by the given redirectURL.
- Card Issuing Bank will send the payment result to OPay.
- OPay will return the client to the merchant returnURL.
Collect your Client's Payment Information
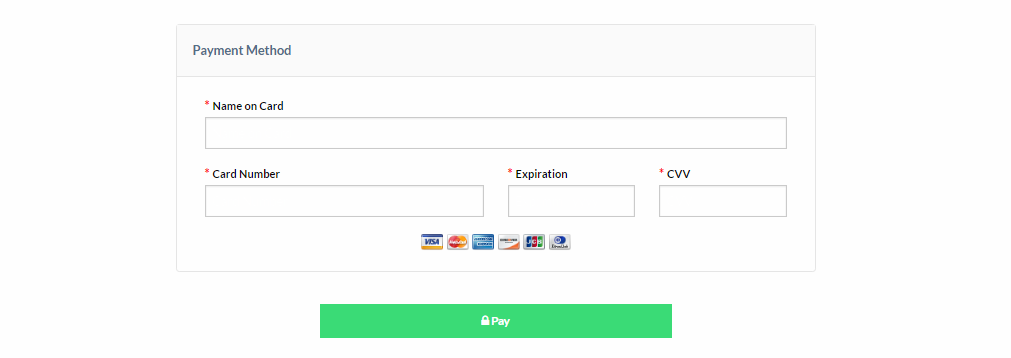
Once your client's Payment information is ready, you will need to present your own payment details form. This form should collect:
- Product Information:
- Name
- Description
- Card Information:
- CVV
- Card Number
- Card Expiry Year
- Card Expiry Month
Create Non-3DS Card Payment
To test your Non-3DS Card Payment, you need to request using the POST method in our sandbox environment.
-Here is the request URL:
https://sandboxapi.opaycheckout.com/api/v1/international/payment/create-Once you have a fully tested payment flow and you are ready for production, use the following production API endpoint URL instead
https://api.opaycheckout.com/api/v1/international/payment/create-Request Parameters:
- Header: Authorization(API Calls Signature), MerchantId
- Json object containing the transaction information:
Authorization    : Bearer {signature}
MerchantId : 256612345678901{
"amount":{
"currency":"EGP",
"total":400
},
"bankcard":{
"cardHolderName":"DAVID",
"cardNumber":"45087***********",
"cvv": "100",
"enable3DS":false,
"expiryMonth":"02",
"expiryYear":"26"
},
"callbackUrl":"https://your-call-back-url.com",
"country":"EG",
"product":{
"description":"description",
"name":"name"
},
"reference":"04123398",
"payMethod":"BankCard",
"returnUrl":"https://your-return-url.com"
}HTTP POST parameters
-Here is a detailed description for the parameters you need to complete the POST request:
-An example of Non-3DS payment request for an amount of 4 EGP is as follows :
class PaymentDsController
{
    private $secretkey;
    private $merchantId;
    private $url;

    public function __construct() {
        $this->merchantId = '281821110129700';
        $this->secretkey = 'OPAYPRV*******0187828';
        $this->url = 'https://sandboxapi.opaycheckout.com/api/v1/international/payment/create';
    }

    public function test(){
        $data = [
            'amount' => [
                'currency' => 'EGP',
                'total' => 400
            ],
            'bankcard' => [
                'cardHolderName' => 'DAVID',
                'cardNumber' => '450875*******',
                'cvv' =>  '100',
                'enable3DS' => false,
                'expiryMonth' => '02',
                'expiryYear' => '26'
            ],
            'callbackUrl' => 'https://your-call-back-url.com',
            'country' => 'EG',
            'payMethod' => 'BankCard',
            'product' => [
                'description' => 'description',
                'name' => 'name'
            ],
            'reference' => '0412339891033312',
            'returnUrl' => 'https://your-return-url.com'
        ]
        ;
        $data2 = (string) json_encode($data,JSON_UNESCAPED_SLASHES);
        $auth = $this->auth($data2);
        $header = ['Content-Type:application/json', 'Authorization:Bearer '. $auth, 'MerchantId:'.$this->merchantId];
        $response = $this->http_post($this->url, $header, json_encode($data));
        $result = $response?$response:null;
        return $result;
    }

    private function http_post ($url, $header, $data) {
        if (!function_exists('curl_init')) {
            throw new Exception('php not found curl', 500);
        }
        $ch = curl_init();
        curl_setopt($ch, CURLOPT_TIMEOUT, 60);
        curl_setopt($ch, CURLOPT_URL, $url);
        curl_setopt($ch, CURLOPT_SSL_VERIFYPEER, false);
        curl_setopt($ch, CURLOPT_SSL_VERIFYHOST, false);
        curl_setopt($ch, CURLOPT_HEADER, false);
        curl_setopt($ch, CURLOPT_RETURNTRANSFER, true);
        curl_setopt($ch, CURLOPT_POST, true);
        curl_setopt($ch, CURLOPT_POSTFIELDS, $data);
        curl_setopt($ch, CURLOPT_HTTPHEADER, $header);
        $response = curl_exec($ch);
        $httpStatusCode = curl_getinfo($ch, CURLINFO_HTTP_CODE);
        $error=curl_error($ch);
        curl_close($ch);
        if (200 != $httpStatusCode) {
            print_r("invalid httpstatus:{$httpStatusCode} ,response:$response,detail_error:" . $error, $httpStatusCode);
        }
        return $response;
    }
    public function auth ( $data ) {
        $secretKey = $this->secretkey;
        $auth = hash_hmac('sha512', $data, $secretKey);
        return $auth;
    }

}
# importing the requests library
import requests
# API Endpoint
URL = "https://sandboxapi.opaycheckout.com/api/v1/international/payment/create"
# defining a params dict for the parameters to be sent to the API
PaymentData = {
'reference' : '12312321324',
'amount': {
"total": '400',
"currency": 'EGP',
},
'product': {
"name": 'Iphone X',
"description": 'xxxxxxxxxxxxxxxxx',
},
'returnUrl' : 'your returnUrl',
'callbackUrl' : 'your callbackUrl',
'userClientIP' : '1.1.1.1',
'country' : 'EG',
'cvv' : '123',
'enable3DS' : 'false',
'expireAt' : ':30',
'expiryMonth' : '11',
'expiryYear' : '25',
'merchantName' : 'your merchant name',
'payMethod' : 'BankCard',
}
# sending post request and saving the response as response object
status_request = requests.post(url = URL, params = json.dumps(PaymentData))
# extracting data in json format
status_response = status_request.json()const request = require('request');
var sha512 = require('js-sha512');
const formData = {
"amount":{
"currency":"EGP",
"total":400
},
"bankcard":{
"cardHolderName":"DAVID",
"cardNumber":"45087***********",
"cvv": "100",
"enable3DS":false,
"expiryMonth":"02",
"expiryYear":"26"
},
"callbackUrl":"https://your-call-back-url.com",
"country":"EG",
"payMethod":"BankCard",
"product":{
"description":"description",
"name":"name"
},
"reference":"041233989101",
"returnUrl":"https://your-return-url.com"
};
var privateKey = "OPAYPRV*******0187828"
var hash = sha512.hmac.create(privateKey);
hash.update(JSON.stringify(formData));
hmacsignature = hash.hex();
console.log(hmacsignature)
request({
url: 'https://sandboxapi.opaycheckout.com/api/v1/international/payment/create',
method: 'POST',
headers: {
'MerchantId': '256621051120756',
'Authorization': 'Bearer '+hmacsignature
},
json: true,
body: formData
}, function (error, response, body) {
console.log('body: ')
console.log(body)
}
)curl --location --request POST 'https://sandboxapi.opaycheckout.com/api/v1/international/payment/create' \
--header 'MerchantId: 256621051120756' \
--header 'Authorization: Bearer 38017496e*******2ab0297d1de8905cb7d85a043d9084254e61a8da6093b6f155550ff51891dca9f9889a' \
--header 'Content-Type: application/json' \
--data-raw '{
"amount":{
"currency":"EGP",
"total":400
},
"bankcard":{
"cardHolderName":"DAVID",
"cardNumber":"450875*******",
"cvv": "100",
"enable3DS":false,
"expiryMonth":"02",
"expiryYear":"26"
},
"callbackUrl":"https://your-call-back-url.com",
"country":"EG",
"payMethod":"BankCard",
"product":{
"description":"description",
"name":"name"
},
"reference":"041233989103331",
"returnUrl":"https://your-return-url.com"
}'import com.google.gson.Gson;
import org.apache.commons.codec.binary.Hex;
import javax.crypto.Mac;
import javax.crypto.spec.SecretKeySpec;
import java.io.*;
import java.net.HttpURLConnection;
import java.net.URL;
import java.nio.charset.StandardCharsets;
import java.util.TreeMap;
import java.util.UUID;
public class PaymentDs {
private static final String privateKey = "OPAYPRV*******0187828";
private static final String endpoint = "https://sandboxapi.opaycheckout.com";
private static final String merchantId = "256621051120756";
public static void main(String[] args) throws Exception {
String addr = endpoint + "/api/v1/international/payment/create";
Gson gson = new Gson();
TreeMap order = new TreeMap<>();
TreeMap amount = new TreeMap<>();
amount.put("currency","EGP");
amount.put("total",new Integer(400));
order.put("amount",amount);
TreeMap bankcard = new TreeMap<>();
bankcard.put("cardHolderName","DAVID");
bankcard.put("cardNumber","450875*******");
bankcard.put("cvv","100");
bankcard.put("enable3DS",Boolean.FALSE);
bankcard.put("expiryMonth","02");
bankcard.put("expiryYear","26");
order.put("bankcard",bankcard);
TreeMap product = new TreeMap<>();
product.put("name","your product name");
product.put("description","your product description");
order.put("product",product);
order.put("callbackUrl","https://your-call-back-url.com");
order.put("country","EG");
order.put("payMethod","BankCard");
order.put("reference", UUID.randomUUID().toString());
order.put("returnUrl","https://your-return-url.com");
String requestBody = gson.toJson(order);
System.out.println("--request:");
System.out.println(requestBody);
String oPaySignature = hmacSHA512(requestBody, privateKey);
System.out.println("--signature:");
System.out.println(oPaySignature);
URL url = new URL(addr);
HttpURLConnection con = (HttpURLConnection)url.openConnection();
con.setRequestMethod("POST");
con.setRequestProperty("Content-Type", "application/json; utf-8");
con.setRequestProperty("Authorization", "Bearer "+oPaySignature);
con.setRequestProperty("MerchantId", merchantId);
con.setDoOutput(true);
OutputStream os = con.getOutputStream();
byte[] input = requestBody.getBytes(StandardCharsets.UTF_8);
os.write(input, 0, input.length);
BufferedReader br = new BufferedReader(new InputStreamReader(con.getInputStream(), StandardCharsets.UTF_8));
StringBuilder response = new StringBuilder();
String responseLine = null;
while ((responseLine = br.readLine()) != null) {
response.append(responseLine.trim());
}
System.out.println("--response:");
System.out.println(response.toString());
//close your stream and connection
}
public static String hmacSHA512(final String data, final String secureKey) throws Exception{
byte[] bytesKey = secureKey.getBytes();
final SecretKeySpec secretKey = new SecretKeySpec(bytesKey, "HmacSHA512");
Mac mac = Mac.getInstance("HmacSHA512");
mac.init(secretKey);
final byte[] macData = mac.doFinal(data.getBytes());
byte[] hex = new Hex().encode(macData);
return new String(hex, StandardCharsets.UTF_8);
}
}using System;
using System.IO;
using System.Linq;
using System.Net;
using System.Text;
using Newtonsoft.Json;
namespace OPayRequest
{
public class Program
{
static void Main(string[] args)
{
PostJson("https://sandboxapi.opaycheckout.com/api/v1/international/payment/create", new opay_request
{
reference = '12312321324',
amount= {
"total"= '400',
"currency"= 'EGP',
},
product= {
"name"= 'Iphone X',
"description"= 'xxxxxxxxxxxxxxxxx',
},
returnUrl = 'your returnUrl',
callbackUrl = 'your callbackUrl',
userClientIP = '1.1.1.1',
country = 'EG';
cvv = '123';
enable3DS = 'false';
expireAt = ':30';
expiryMonth = '11';
expiryYear = '25';
merchantName = 'your merchant name';
payMethod = 'BankCard';
});
}
private static void PostJson(string uri, opay_request postParameters)
{
string postData = JsonConvert.SerializeObject(postParameters);
byte[] bytes = Encoding.UTF8.GetBytes(postData);
var httpWebRequest = (HttpWebRequest) WebRequest.Create(uri);
httpWebRequest.Method = "POST";
httpWebRequest.ContentLength = bytes.Length;
httpWebRequest.ContentType = "text/json";
using (Stream requestStream = httpWebRequest.GetRequestStream())
{
requestStream.Write(bytes, 0, bytes.Count());
}
var httpWebResponse = (HttpWebResponse) httpWebRequest.GetResponse();
if (httpWebResponse.StatusCode != HttpStatusCode.OK)
{
string message = String.Format("GET failed. Received HTTP {0}", httpWebResponse.StatusCode);
throw new ApplicationException(message);
}
}
}
public class opay_request
{
public string reference { get; set; }
public string returnUrl { get; set; }
public string callbackUrl { get; set; }
public string userClientIP { get; set; }
public string expireAt { get; set; }
public string country { get; set; }
public string cvv { get; set; }
public string enable3DS { get; set; }
public string expireAt { get; set; }
public string expiryMonth { get; set; }
public string expiryYear { get; set; }
public string merchantName { get; set; }
public string payMethod { get; set; }
public product product;
public amount amount;
}
public class amount
{
public string total { get; set; }
public string currency { get; set; }
}
public class product
{
public string name { get; set; }
public string description { get; set; }
}
}Header must contain the "Signature" , "MerchantId"
Signature is calculated using SHA-512 HMAC signed with your Private Key. See API Calls Signature section for more details.
Non-3DS Card Payment Response
-Response Parameters:
the parameters contained in the response received whenever you call the Non-3DS payment API as a JSON Object.
{
    "code": "00000",
    "message": "SUCCESSFUL",
    "data": {
        "reference": "937102167",
        "orderNo": "211004140885521681",
        "status": "SUCCESS",
        "amount": {
            "total": 400,
            "currency": "EGP"
        },
        "vat": {
            "total": 0,
            "currency": "EGP"
        }
    }
}
-Here is a detailed description for the parameters received in the response:
| Parameter | type | Description | example | |
|---|---|---|---|---|
| reference | String | Unique merchant payment order number. | 937102167 | |
| orderNo | String | Unique Opay payment order number. | 211004140885521681 | |
| status | enum | [INITIAL, PENDING, SUCCESS, FAIL, CLOSE] | SUCCESS | |
| amount | ||||
| total | Integer | amount(cent unit). | 400 | |
| currency | String | currency type.See full list here | EGP | |
| vat | ||||
| total | Integer | amount(cent unit). | 10 | |
| currency | String | currency type.See full list here | EGP | |
| failureCode | String | fail error code. | payment fail error code, not blank when status [FAIL/CLOSE] | |
| failureReason | String | fail error message. | payment fail error message, not blank when status [FAIL/CLOSE] | |
Error Handling
After submitting an API call to OPay, you receive a response back to inform you that your request was received and processed. A successful OPay API should return a status code 00, meanwhile, in a situation where any payment processing error occurred, you will receive an error code with a message to describe the reason of the error. A sample error response can be found below.
{
    "code": "02004",
    "message": "the payment reference already exists."
}
Depending on the HTTP status code of the response, you should build some logic to handle any errors that a request or the system may return. A list of possible potential error codes that you may receive can be found below. A full list of all possible error codes can be found in the Error Codes section.
| Error Code | Error Message |
|---|---|
| 02000 | authentication failed. |
| 02001 | request params not valid. |
| 02003 | payMethod not support. |
| 02004 | the payment reference already exists. |
| 02002 | merchant not configured with this function. |
| 02007 | merchant not available. |
| 50003 | service not available, please try again. |